Free cybersecurity assessment for companies
5 details about your company and 25 questions on 8 topics to see where to start: between 10 and 15 minutes. Your score appears on screen, free, with no email or account needed.
If you do not know an answer, choose “I don't know”. It is prepared by Minery Report, a cybersecurity consultancy in Madrid. It is guidance, not an audit.
You can close the tab and carry on in this same tab within two hours.
What it measures
Eight sections with a company's basic cybersecurity measures. Each question has closed answers, plus “I don't know”, and a help note in case a term is unfamiliar.
- Governance: who decides and is accountable
- Knowing what you have
- Who gets in and how
- Devices protected and up to date
- Email, payments and your internet presence
- Recovering if you are brought to a halt
- Detecting and responding
- People and suppliers
Who it is for
For management, IT leads and the self-employed who want a first picture of their basic cybersecurity measures and to know where to start. You do not need to be technical: every question has a help note and accepts “I don't know”. If you already have a security lead, it helps them prepare the conversation with management.
What you get
On screen and with no email: your level, your score, how each section comes out, the main risks and where to start. If you give us your domain, you will see separately what it shows publicly. You can print the result or save it as a PDF.
If you wish, when you finish we can also email you a fuller PDF report, with a summary for management, a 90-day plan and steps for your technical team.
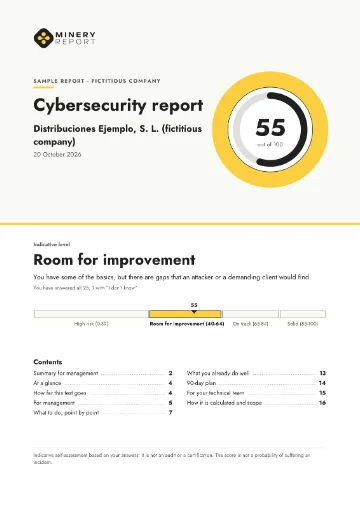 What the report looks likeThe report of a fictitious company, produced by the same assessment: a summary for management, a 90-day plan and steps for your technical team.See a sample report (PDF, 16 pages, 270 KB) (opens in a new tab)
How it is calculated
Each answer adds in full, adds half or adds nothing. If something basic is missing, the level does not go up even if the rest is fine. The detail is in the frequently asked questions.
How it relates to CIS, ISO 27001, NIS2 and DORA
The questions relate to controls in the CIS Critical Security Controls v8.1, ISO/IEC 27001:2022, the NIS2 Directive, the Digital Operational Resilience Act (DORA) and Spain's National Security Framework (ENS), which applies to the Spanish public sector and the companies that work for it. The relationship is thematic and, in general, partial. The assessment does not tell you whether a rule applies to you or evaluate compliance with it.
What it is not
This is an indicative self-assessment based on your answers and on public information about your domain. It is not an audit, it does not certify compliance with any standard or law and it does not replace a professional assessment. References to frameworks show which controls each answer relates to, not that you comply or fail to comply.
Frequently asked questions about the assessment
Yes. The assessment and the on-screen result are free, and you do not need to create an account or leave your email address to see it.
5 details about your company and 25 closed questions in 8 sections, each with “I don't know” and a help text: between 10 and 15 minutes, at your own pace. When you finish, you see on screen your level, your score, how each section comes out, your main risks and where to start.
This is a self-assessment: you answer and we do not check anything inside your systems. An audit reviews your controls against evidence within an agreed scope, and a penetration test tries to exploit real weaknesses in your systems with your permission. This is an indicative self-assessment based on your answers and on public information about your domain. It is not an audit, it does not certify compliance with any standard or law and it does not replace a professional assessment. References to frameworks show which controls each answer relates to, not that you comply or fail to comply.
In this assessment, seven controls are essential: an accountable person with follow-up by management, two-step verification, protection against malware, updates, a backup out of reach of an attack, a tested restore and an incident response plan. If one is missing, your level is capped even if your score is high.
Each answer is worth 100, 50 or 0, and each question has a weight from 1 to 3 according to its importance. The score is the weighted average. The level comes from the score: High risk (up to 39), Room for improvement (40-64), On track (65-84) and Solid (85 or more). Seven controls are essential: if one is missing, or only partly in place, the level is capped even if the score is high, and we explain why. “I don't know” counts as zero and is shown separately; for an essential control, the level is also provisional and cannot go above On track.
It counts as zero, because not knowing is also a visibility gap, but we show it separately: we have not checked that the control is missing. If you do not know about one of the seven essential controls, it counts as zero, your level is shown as provisional and it cannot go above On track, just as if the control were only partly in place.
Only if you enter it: the public configuration of your email and website (SPF, DKIM, DMARC, DNS and website headers), with low-intensity queries. We do not scan ports or look for vulnerabilities. You will see it separately in your result and it does not change your score.
It gives you a first picture. The questions relate to controls in the CIS Controls, ISO/IEC 27001, NIS2, DORA and Spain's National Security Framework (ENS), but the assessment does not tell you whether a rule applies to you or evaluate compliance with it.
On this English page your on-screen result is calculated in your browser and your answers are not sent to our server. We do not ask for any data that identifies you: only your sector, your size and your answers, as closed options. While you take the assessment, your progress is saved only in this browser and is deleted when you see the result or after two hours. If you enter a domain, it is sent to our server only to run the public checks and it is not stored. Only if you request the report by email do we store your answers, linked to your email address, to prepare it, send it to you and give you access to it, as explained in the privacy information of the form.
Yes, whenever you like. The on-screen result stays only in this tab for up to two hours after you start: if you close it, you will have to answer it again.
Minery Report, a cybersecurity consultancy in Madrid, Spain: 30 professionals and more than 100 clients. The assessment is guidance, not an audit.